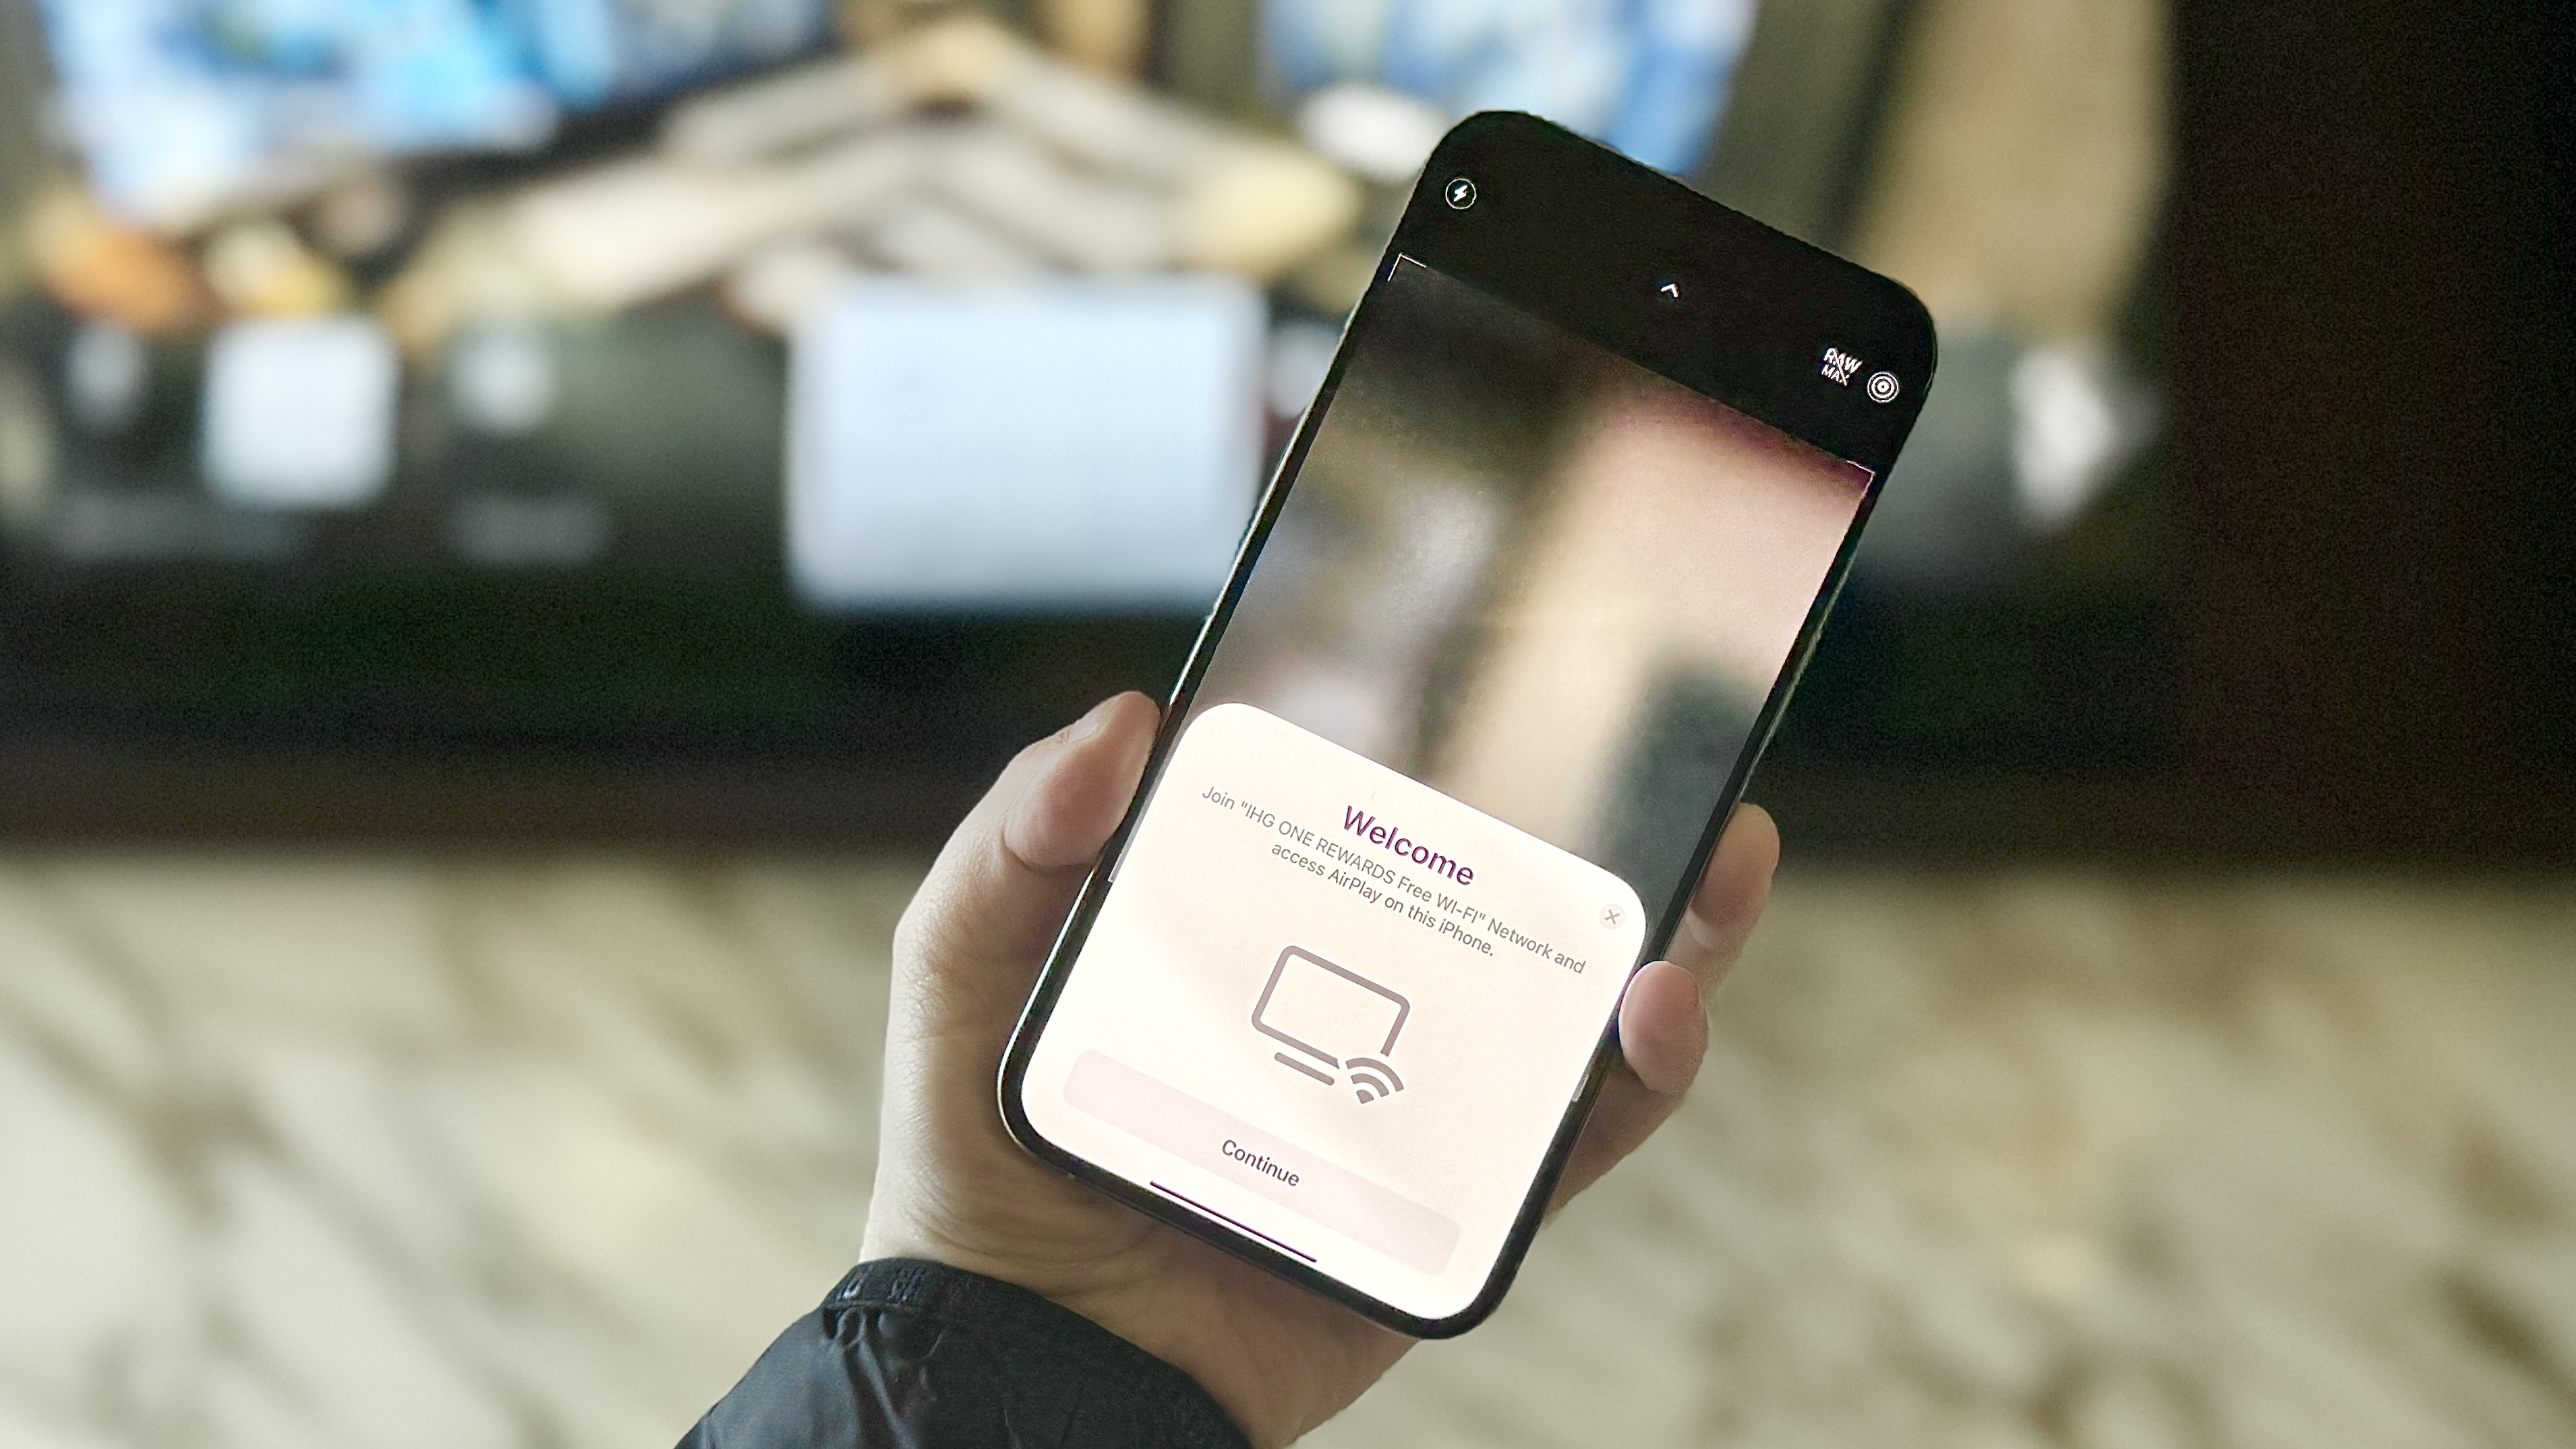
Millions of AirPlay-enabled devices were at risk for months as Apple and security researchers at Oligo worked together to develop and roll out patches for a collection of bugs the researchers dubbed “AirBorne.”
The bugs discovered by the Oligo team would essentially permit any threat actor connected to the same Wi-Fi network as a third-party AirPlay enabled device to run their own code on it. That means anyone connected to the same Wi-Fi as a smart TV, speaker or set-top box at a party, could potentially use that open AirPlay connection to spread malicious code from one device to another.