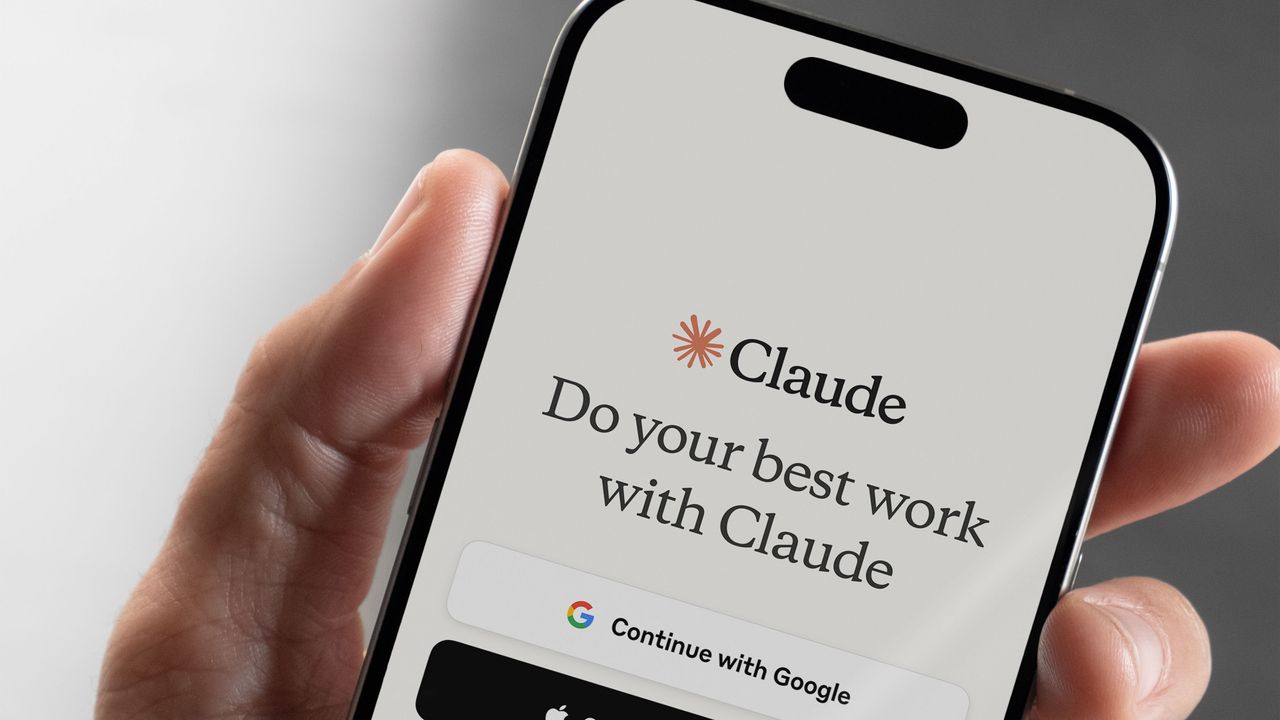
- Huntress spots malicious Claude Artifact spoofing Claude Desktop, spreading SectopRAT malware
- Victims were redirected via Bing ads, infecting at least 29 organizations between July 21–22, 2026
- Claude removed the artifact after 7,000+ views; malvertising risks persist despite disclaimers on artifacts
At least 29 organizations have been infected with a Remote Access Trojan (RAT) after mistaking a public Claude Artifact for a legitimate Claude page.