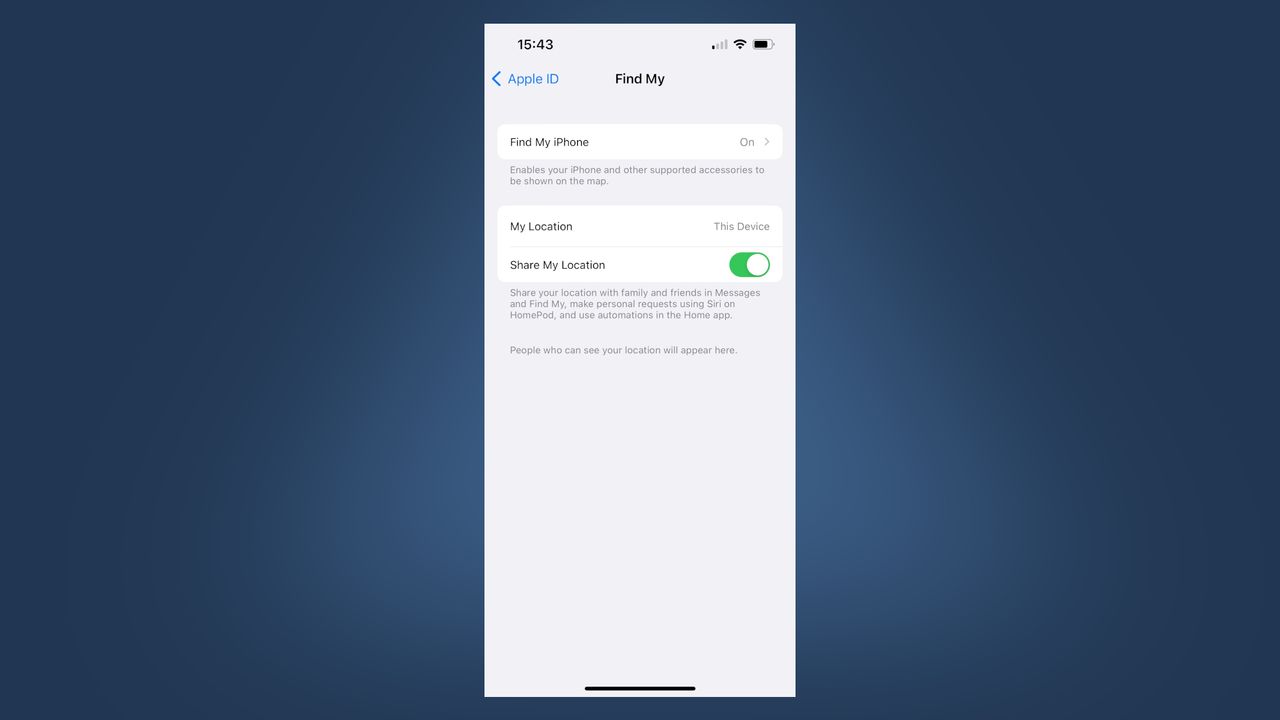
- Researcher registers Linux machine as a trusted device on Apple's Find My network and pulled live people-tracking data that Apple normally reserves for its own hardware
- The work is not a mass-surveillance exploit: it is limited in scope and only reads a location share that a friend had already agreed to, and it cannot silently locate arbitrary Apple users
- The approach took less than a week of protocol reverse engineering, and Apple has maintained silence on queries about the technique employed
Apple keeps the full Find My experience locked to its own devices, but a recent attempt by security researchers suggests that wall may be a relatively weak barrier to entry.