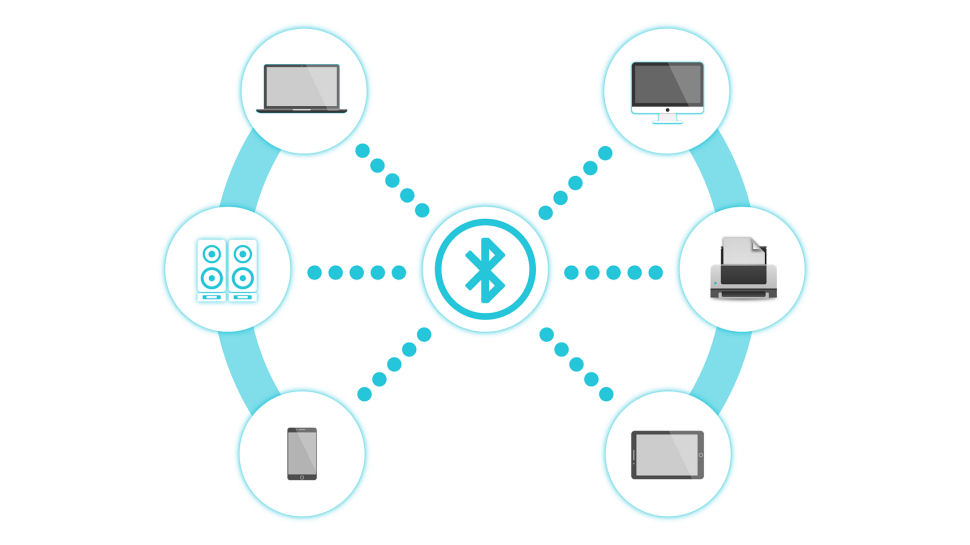
Experts have uncovered a way to trick a Bluetooth-enabled device into thinking it has connected to a wireless keyboard when, in fact, it’s connecting to another computer.
This, in turn, would allow the operator to run commands on the device, including running malware, according to cybersecurity researcher Marc Newlin, who discovered the flaw and disclosed it to Bluetooth software vendors last summer.