- TP-Link patched four Omada gateway flaws, two rated critical for code execution
- Three were command injection bugs; one allowed root shell via privilege mismanagement
- Multiple models affected; one critical flaw requires no authentication for exploitation
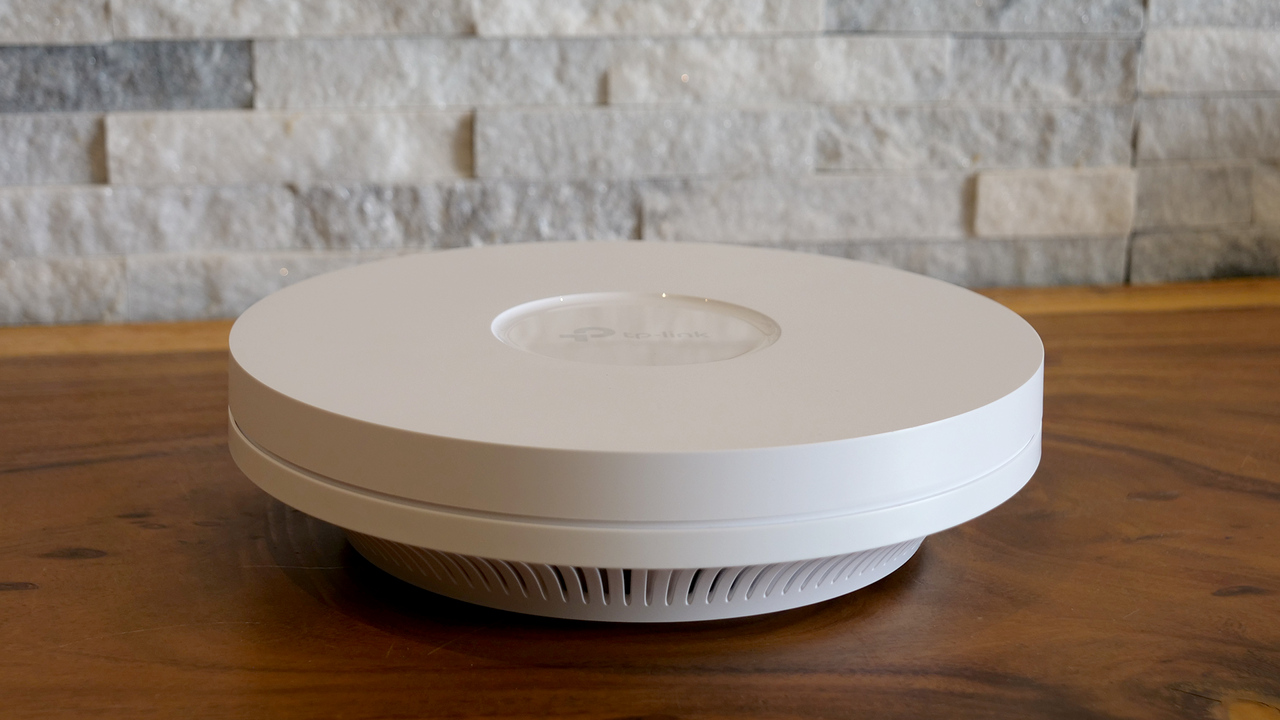
Network gear manufacturer TP-Link has patched four vulnerabilities discovered in its Omada gateway products, including two critical severity ones that could allow arbitrary code execution.